Leave Your Message

What Is a Juniper Enterprise Smart Router?

Enterprise networks are carrying more applications, devices, and encrypted traffic than traditional branch routers were designed to handle. Ericsson’s November 2024 Mobility Report forecasts mobile data traffic to nearly triple between 2023 and 2029. Cisco’s Annual Internet Report also projected 29.3 billion networked devices by 2023. These figures show why routing now involves more than forwarding packets between offices.

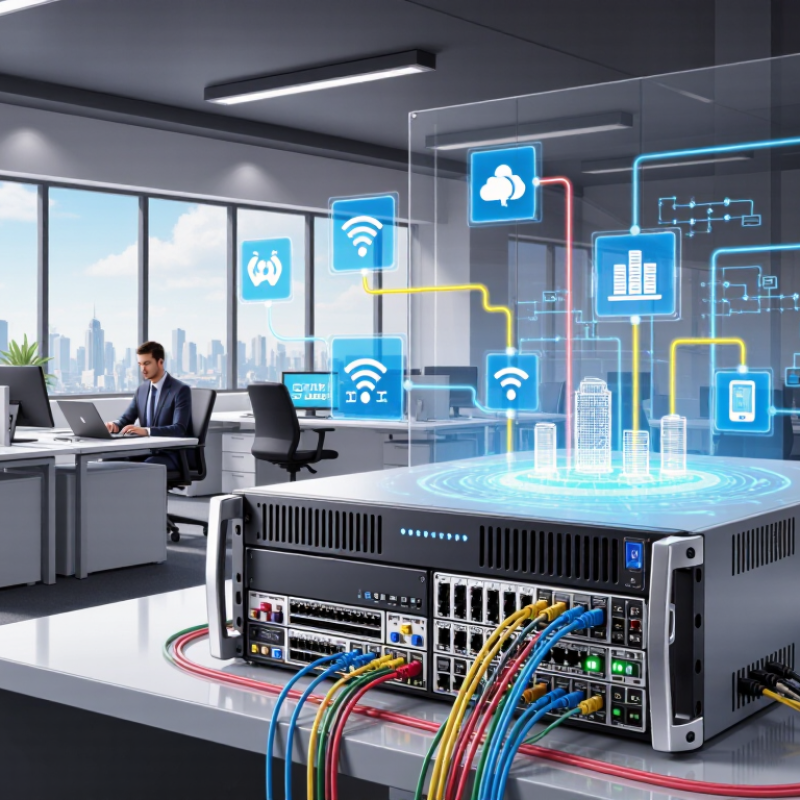
A Juniper Enterprise Smart Router is best understood as an intelligent routing platform for business networks. It can connect branches, campuses, data centers, cloud services, and remote users through policy-based decisions. Juniper’s Session Smart Router focuses on application-aware connectivity, zero-trust principles, and software-defined WAN control. When combined with Juniper Mist WAN Assurance, administrators can use telemetry and artificial intelligence to identify latency, packet loss, or unstable links. A practical example is a retail branch switching from broadband to LTE when its primary circuit fails.

It is not simply a faster box.

The term “Juniper Enterprise Smart Router” may sound like one fixed product name, but that interpretation can be incomplete. Juniper’s enterprise portfolio includes different platforms, licensing models, and deployment options. Buyers should verify the exact hardware, software release, throughput, security features, and support terms. Gartner’s Market Guide for SD-WAN emphasizes centralized policy, application visibility, and operational simplicity as important evaluation areas. Yet automation is not magic. Poor segmentation or inaccurate application policies can still create outages. A reliable assessment therefore combines vendor documentation, independent testing, and real traffic measurements before deployment.
What Is a Juniper Enterprise Smart Router?

What Defines a Juniper Enterprise Smart Router: Architecture and Purpose

An enterprise smart router is a purpose-built network platform, not merely a faster office gateway. Its architecture separates packet forwarding from route calculation and device management. The forwarding plane moves traffic through hardware at line rate. The control plane selects paths using routing protocols and policy. The management plane handles configuration, monitoring, and software updates. That separation matters. It helps teams change network policy without manually touching every packet path, though poor configuration can still disrupt service.

The design also combines routing with practical controls: network segmentation, traffic prioritization, encrypted connections, and failover links. These features help keep voice calls clear while large files move, or redirect traffic when a circuit fails.

The ITU’s Facts and Figures 2024 estimated that 5.5 billion people, or 68% of the world’s population, were online.

More connected users and services make predictable network performance increasingly important. Uptime Institute’s 2024 outage analysis found that more than half of significant outages cost over $100,000. That figure is not a router score; outages have many causes. Still, resilience deserves attention.

A smart router can provide visibility and alternate paths, but it cannot correct a flawed network plan by itself. Some deployments also need careful tuning, a detail easy to underestimate.
How Junos OS Uses BGP-4 (RFC 4271) and 128-Bit IPv6 Routing

An enterprise smart router connects separate networks and decides where traffic should go. Its routing software can use BGP-4, defined in RFC 4271, to exchange reachability information between autonomous systems. BGP is a path-vector protocol: routers share network prefixes and attributes, then apply policies to select usable routes. It does not simply choose the path with the fewest hops. A policy change can redirect traffic, so operators need clear rules and careful review. Small details matter.

IPv6 uses 128-bit addresses, giving routers a much larger address space than IPv4. In practice, routing decisions use prefixes, such as a network address paired with a prefix length, rather than treating every address as a separate destination. The router’s control plane processes route updates, while its forwarding plane sends packets through the selected interface. That distinction matters when diagnosing a route that appears in a table but does not carry traffic. Monitoring helps, but it cannot replace testing. I still find that prefix planning is easy to underestimate; a tidy address plan can become awkward as networks grow.

How SD-WAN Uses NIST SP 800-207 Zero-Trust Principles

An enterprise smart router is more than a traffic switch. In an SD-WAN, it can apply access policies, connect branch offices through encrypted tunnels, and send network activity to central monitoring. NIST SP 800-207 says zero trust should grant access based on verified users, devices, and context—not simply network location. A router can help enforce those decisions, but it cannot create zero trust alone.

That distinction matters. Verizon’s 2024 Data Breach Investigations Report found that the human element was involved in 68% of breaches. IBM’s 2024 Cost of a Data Breach Report put the global average breach cost at $4.88 million. These figures are not proof that SD-WAN prevents breaches; they show why organizations need layered controls. Check device health, limit access to specific applications, and log policy decisions across branches. A policy that looks perfect on paper can still miss an unmanaged laptop or a forgotten exception. That deserves regular review.

Tips: Start with one branch and a small set of sensitive applications. Test access rules, inspect logs, and confirm that a compromised device cannot reach unrelated systems. Then refine the policy.

Which Metrics Matter: 1/10/25/100/400GbE and 99.999% Availability

A Juniper enterprise smart router is best judged by measurable performance, not its port list. The 1, 10, 25, 100, and 400GbE options describe link speeds, not guaranteed application throughput. Check forwarding capacity with realistic packet sizes, security policies, and concurrent sessions enabled. A 400GbE uplink can still disappoint when slower interfaces, congestion, or route processing become bottlenecks. Test latency and packet loss during busy periods, too. Small packets expose limits that headline bandwidth can hide.

Availability matters just as much. 99.999% uptime allows roughly 5.3 minutes of downtime per year, before clarifying maintenance exclusions and measurement boundaries. The 2024 Uptime Institute outage analysis reported that 54% of respondents’ most significant outages cost more than $100,000. That figure makes failover design a practical concern, not a vanity metric. Still, five nines on paper can mislead if power, upstream links, or monitoring remain single points of failure. I would verify recovery with a timed failover test; lab results rarely capture every messy edge case.

Tips: Match port speed to actual traffic growth, and record latency, loss, and failover time at peak load. Ask for test conditions. Compare like with like. One caveat: projected demand is easy to overstate, so leave room for review.

How to Assess Automation, Security, and Lifecycle Support Step by Step

An enterprise smart router connects offices, cloud services, and remote users while applying centrally managed policies. Assess automation with a small pilot: configure a test branch, change a routing rule, and verify that logs record who changed what. Small test first. Confirm templates support approval steps, version history, and rollback. Automation saves repetitive work, but it can also spread a faulty rule quickly. Check the rollback.

Next, examine security at the device and network levels. Look for role-based access, encrypted management, multifactor authentication, and clear alerts for unusual configuration changes. Ask whether the router can segment guest devices from finance systems, then test that separation with actual traffic. The 2024 Cost of a Data Breach report estimated the global average breach cost at $4.88 million. That figure makes audit trails and timely patching practical risk controls, not decorative features.

Finally, assess lifecycle support before purchase. Request the published support period, software update cadence, vulnerability notification process, and replacement options. Check how long critical fixes remain available, and whether older hardware can handle planned growth. A feature-rich router may still become a poor choice if support ends before a site refresh. I would also test failover during a quiet maintenance window; paper specifications rarely reveal every awkward edge case.

What Is a Juniper Enterprise Smart Router? — How to Assess Automation, Security, and Lifecycle Support Step by Step

An enterprise smart router is a network device that forwards traffic and may also provide routing, policy enforcement, monitoring, and programmable management. Use the checks below to assess capabilities without relying on product claims alone.

Step Assessment dimension What to check Evidence to request or test Practical acceptance indicator
1 Define the role Identify required routing, WAN and LAN interfaces, throughput, routing scale, redundancy, and traffic-management functions. Architecture diagram, interface specifications, routing-protocol support, and performance figures with stated test conditions. Requirements are mapped to documented capabilities; performance is evaluated with the intended feature set enabled.
2 Check automation interfaces Look for machine-readable configuration and state access, such as NETCONF (RFC 6241), RESTCONF (RFC 8040), and YANG data models (RFC 7950), where supported. API or protocol documentation, supported data models, authentication options, and a test that reads device state and applies a controlled change. A script can retrieve structured state and make a documented change without relying solely on interactive command-line entry.
3 Validate safe change workflows Assess configuration validation, change review, commit behavior, rollback or recovery options, and whether repeated automation runs produce the intended state. A lab demonstration of a valid change, an invalid change, and recovery from a deliberately introduced configuration error. Changes can be tested and audited, errors are reported clearly, and a documented recovery path is available.
4 Review access security Check role-based access, individual accounts, centralized authentication options, secure administrative access, and controls for unused services. Access-control configuration, authentication integration guidance, management-plane exposure review, and a test confirming permissions differ by role. Administrative access is restricted to approved paths and accounts receive only the privileges required for their tasks.
5 Assess encryption and security protocols Verify secure management transport and, where required, encrypted network tunnels. SSH is specified in RFC 4253; IPsec architecture is specified in RFC 4301. Supported protocol and algorithm documentation, configuration examples, and a test that confirms insecure management services can be disabled. Required traffic and management sessions use approved secure protocols and settings; obsolete or unneeded services can be turned off.
6 Test monitoring and auditability Check event logging, time synchronization, monitoring interfaces, alerting, and the ability to trace administrative changes. Sample logs and alerts; syslog message format support can be compared with RFC 5424, and SNMPv3 security capabilities with RFC 3414. Events include useful timestamps and identifiers and can be forwarded to the organization’s monitoring and log systems.
7 Review resilience and recovery Evaluate power and link redundancy, routing convergence expectations, configuration backup, software recovery, and documented failover behavior. Failure-test plan, backup and restore procedure, and observed results from a controlled link or node failure. Recovery behavior is measured against the organization’s own availability targets and verified in a representative test.
8 Confirm software and vulnerability handling Establish how security advisories, vulnerability fixes, software images, and upgrade instructions are published and verified. Advisory history, image-integrity verification instructions, upgrade and downgrade guidance, and a maintenance-window test plan. The organization can identify affected software, obtain a supported fix, verify the image, and plan a tested upgrade or recovery.
9 Verify lifecycle support Check the published support period for the specific hardware and software version, including end-of-sale, end-of-support, and replacement planning information. Dated lifecycle notices, support terms, software maintenance policy, and confirmation of access to technical support and security updates. The intended deployment period fits within documented support dates, with a practical upgrade or replacement path.
10 Make a deployment decision Compare test results with documented network, security, operations, and lifecycle requirements; record any gaps and mitigations. Completed assessment, lab results, risk register, operating procedures, and an approved maintenance plan. Approval is based on measured requirements and documented evidence, not on feature names alone.